

Cyber: Governance of the Security Supply Chain
Session Overview
Cybersecurity risks in crypto-asset services increasingly arise not only from vulnerabilities in blockchain protocols or the compromise of signing keys, but from dependencies across the wider operational and technology supply chain: wallet-system vendors and their staff, cloud and CI/CD environments, transaction-generation processes, administrative privileges, smart contracts, oracles and bridges — and, as October 2026 has shown, the physical distribution channel for the hardware wallets that hold the keys.
The session starts from the work already done. After the May 2024 DMM Bitcoin loss, which was traced to a compromise at a wallet-system vendor outside the regulatory perimeter, JPCrypto-ISAC documented a third-party (vendor) management guideline for crypto-asset businesses, built on the FISC framework, with an MOU template and a control checklist; it was presented to BGIN at Block 14. Takaya Sugino (Japan Financial Services Agency) will then present the JFSA's April 2026 policy on strengthening cybersecurity at crypto-asset exchange service providers — self-help, mutual aid and public support, including raising the supervisory guideline's expectations for external audit and outsourcing management — and the June 2026 research paper Cybersecurity Issues and Countermeasures in Crypto-Asset-Related Businesses commissioned under it.
The room will then take up the hardware-wallet supply-chain incident reported in October 2026, in which devices sold through third-party resellers carried covert implants that captured recovery phrases at setup — an attack that left the secure element, firmware and genuine-device check intact — and ask what it adds to the picture: distribution-channel assurance, device provenance and tamper evidence, and the limits of attestation.
Finally, participants will discuss which additional perspectives the BGIN security-supply-chain document needs beyond vendor management (open-source and software components, SBOM, hardware and distribution channels, DeFi and cross-chain dependencies, assurance and certification) and confirm the roadmap, owners and timeline toward publication.
Agenda
- Introduction (Shin'ichiro Matsuo): where the work stands — the third-party management guideline documented after the DMM Bitcoin incident (JPCrypto-ISAC, presented at Block 14) and what BGIN has covered so far.
- JFSA presentation (Takaya Sugino): the April 2026 policy on strengthening cybersecurity at crypto-asset exchange service providers, and the June 2026 research paper on cybersecurity issues and countermeasures in crypto-asset-related businesses.
- Discussion: the October 2026 hardware-wallet distribution incident — implants inserted through reseller channels, what genuine-device checks can and cannot detect, and what operators, vendors and resellers should each be accountable for.
- Discussion: additional perspectives for the BGIN security-supply-chain document beyond vendor management — open-source and software components (SBOM), hardware and distribution channels, cloud and CI/CD, DeFi and cross-chain dependencies, assurance and certification.
- Roadmap toward publication: document scope and structure, editors and section owners, WG-call schedule, and the review cycle after Block 15.
Session Chair & Speakers
Session Chair
Shin'ichiro Matsuo (Georgetown University)
Speakers
Takaya Sugino (Japan Financial Services Agency)
Related Documents
Session introduction slides — Shin'ichiro Matsuo (Session Chair)
Type: PDF
Presentation: Crypto Asset Cybersecurity — Takaya Sugino (Japan Financial Services Agency)
Type: PDF
Cybersecurity Issues and Countermeasures in Crypto-Asset-Related Businesses — Research paper, June 30, 2026 (Deloitte Tohmatsu LLC)
Type: PDF
JFSA: Policy on Strengthening Cybersecurity at Crypto-Asset Exchange Service Providers, April 3, 2026 (Japanese)
Type: Policy
Block 14 MR: Governance of Security Supply Chain
Type: Meeting Report
Block 13 MR: Governance of Security Supply Chain
Type: Meeting Report
Venue
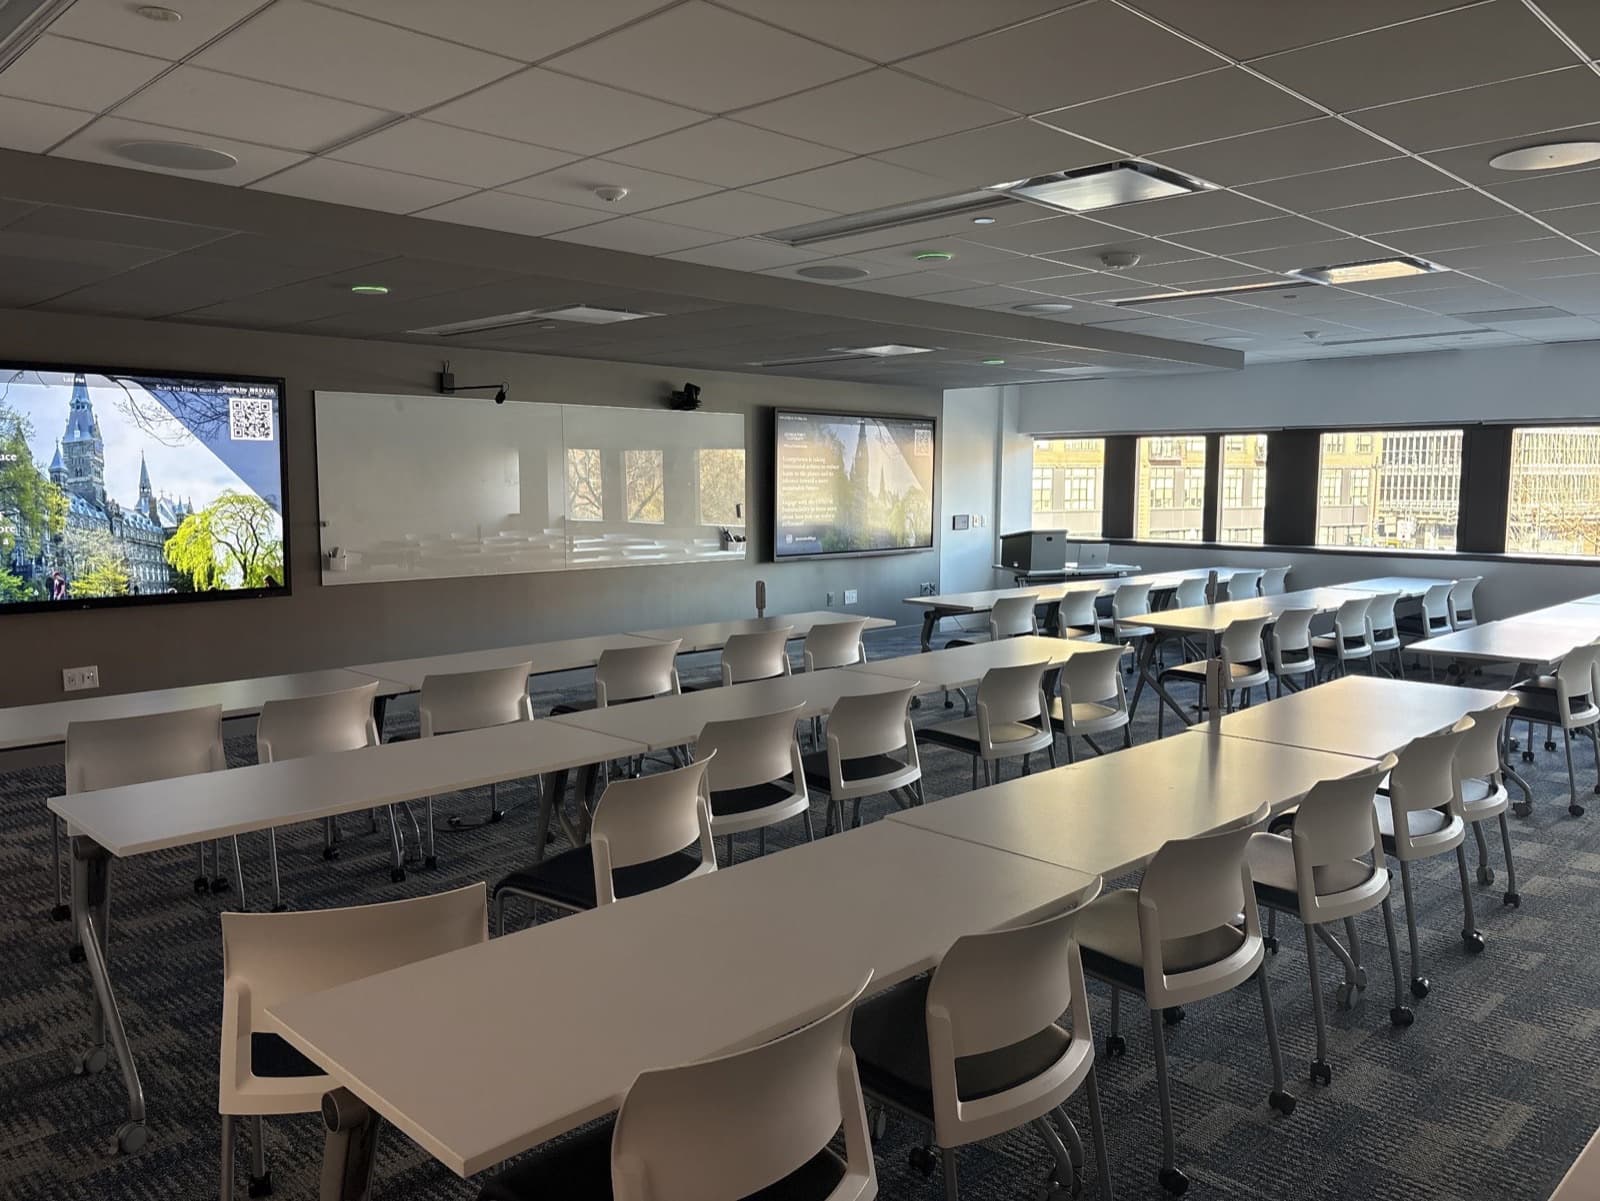
Location: Capitol Campus — Room A (2424)
Address: 111 Massachusetts Avenue NW, Washington, DC 20001, United States
Georgetown University Capitol Campus · Washington, D.C.
Access & venue details →Working Group
Cybersecurity Working Group
Addresses security frameworks, threat intelligence, and cybersecurity standards for blockchain systems
- Tomofumi Okubo
- Takaya Sugino